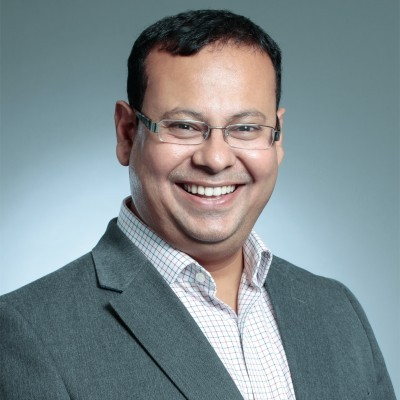
Vijay Mitra
Head of AI and Digital Risk Nationwide Building Society
Vijay Mitra is a recognised leader in Responsible AI Governance, and Head of AI & Digital Risk at Nationwide Building Society. Operating at Director level, he shapes enterprise AI strategy, driving how innovation, regulation, and trust converge in practice. With over two decades of experience, including senior roles at HSBC, he advises on AI adoption and regulatory expectations across FCA, PRA, and the EU AI Act. Vijay brings a board-level perspective on AI governance and risk appetite and is a sought-after thought leader and speaker. In a voluntary capacity, he leads the AI Panel at WCIT Livery, advancing responsible AI adoption across the City of London.
Agenda Day 1
11:30 AM Panel Debate – Build, Buy, or Bluff? The Reality of in House AI Red Teaming
AI dramatically expands the attack surface, yet the skills required to test these systems remain scarce. Enterprises are under pressure to build internal capability, but few understand what AI red teaming requires in practice. This debate challenges assumptions around in house readiness and exposes where maturing may be overestimated. Panellists will discuss the feasibility of building internal AI red teams, the tooling and expertise genuinely required, and where external specialists remain critical.
3:00 PM Networking Roundtable Discussions
Join relaxed, topic-led roundtables designed to connect you with peers facing similar challenges in securing AI across the enterprise. In a no-slide, no-stage setting, each table will tackle a timely Secure AI theme. Lightly moderated to spark honest discussion, challenge assumptions, and share what's really happening on the ground.
4:30 PM Closing Panel Debate – Defining the Risk Landscape: Securing Enterprise AI in 2026
Enterprise AI is already in production, but security models haven't caught up. Teams are deploying copilots, agents, and AI-powered workflows faster than organisations can define acceptable risk, leading to inconsistent decisions and growing exposure. The challenge isn't understanding every AI threat, it's deciding where to draw the line and enforcing it consistently. This panel focuses on a critical question: how do organisations define and apply AI risk boundaries in practice, across data use, model behaviour, and autonomy, without slowing down delivery?
Check out the incredible speaker line-up to see who will be joining Vijay.
Download The Latest AgendaIn Partnership With:

QUESTIONS?
Address: IQPC Ltd, 129 Wilton Road,
London SW1V 1JZ
Telephone: 44 (0) 207 368 9300
Fax: 44 (0) 207 368 9301
Email: enquire@iqpc.co.uk

©2026 IQPC. All rights reserved.


