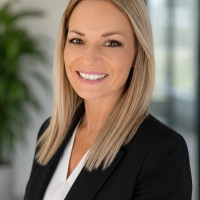
Orsolya Salla
Director - Head of Data Privacy Independent
Conference Day 1: Tuesday 13th October 2026
11:30 AM Making AI and Data Products Work in a Regulated World: Privacy, Risk, and Real-World Trade-offs
As organisations accelerate AI adoption and scale data products globally, data privacy
and regulatory pressure are moving from a compliance exercise to a core part of how
these systems are designed and operated. What works in one market may not be viable
in another, and decisions made centrally must still be implemented in a way that meets
local legal and regulatory requirements. Orsolya Salla shares how large organisations are
navigating this complexity, working across business, HR, legal, and data teams to enable
AI-driven use cases while managing risk. With evolving frameworks such as GDPR and the
EU AI Act, the challenge is no longer whether to act, but how to balance innovation with
accountability in environments where the consequences of getting it wrong are significant.
• Aligning global data and AI initiatives with local privacy, regulatory, and compliance
requirements
• Embedding privacy, legal, and governance considerations into data product and AI
development from the outset
• Managing risk, accountability, and communication as AI use cases expand across the
organisation
Check out the incredible speaker line-up to see who will be joining Orsolya.
Download The Latest AgendaIn Partnership With:

QUESTIONS?
Address: IQPC Ltd, 129 Wilton Road,
London SW1V 1JZ
Telephone: 44 (0) 207 368 9300
Fax: 44 (0) 207 368 9301
Email: enquire@iqpc.co.uk

©2026 IQPC. All rights reserved.


