Responsible AI Summit Main Conference Day 1 - Monday 21 September
Morning Plenary Session
8:00 am - 8:45 am
Registration & Breakfast
8:45 am - 9:00 am
Chairs Opening Remarks
Suzanne Brink -
Head of Responsible AI,
Lloyds Banking Group
9:00 am - 9:30 am
Opening Panel Discussion – Behind Closed Doors: The Real AI Conversations in the Boardroom
Ajay Chakravarthy -
Chief AI Officer,
Thales
Rebecca Salsbury - Chief Product and Technology Officer, Financial Times
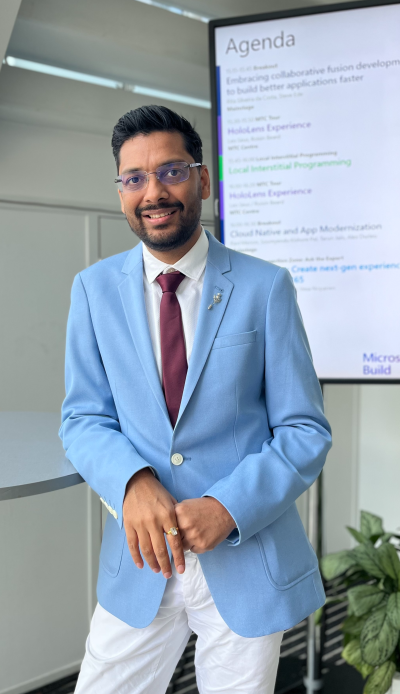
Sray Agarwal - Head of Infosys Responsible AI Office (EMEA), Infosys
In boardrooms, AI discussions are no longer abstract, they are charged with urgency, competing priorities, and hard trade-offs. C-suite leaders are navigating pressure to move fast while confronting rising demands for accountability, safety, and trust. This opening panel sets the scene for 2026 and explores the tensions shaping those conversations, how executives are interpreting "Responsible AI," and where alignment, and friction, is emerging at the top.
· Balancing speed with accountability in AI adoption.
· Interpreting Responsible AI across competing executive priorities.
· Managing trade-offs between innovation, risk, and governance.
9:30 am - 10:00 am
From Responsible AI to Responsible Autonomy: Are We Ready for AI That Acts?
Syed Quiser Ahmed -
AVP, Global Head of Infosys Responsible AI Office,
Infosys
AI is moving from systems that generate answers to agents that can make decisions, access systems, and take actions on our behalf. This changes the Responsible AI challenge from asking whether an AI output is trustworthy to asking whether the autonomous system itself is safe, bounded, secure, and accountable. The keynote will explore what "meaningful human control" should look like in an agentic world, and whether today's governance frameworks are sufficient for AI that can act independently. The central question: How do we enable autonomy without giving up control?
Sponsored by: Infosys
10:00 am - 10:30 am
Afternoon Plenary Keynote – Scaling Responsible AI: From Guidance to Practice
Suzanne Brink -
Head of Responsible AI,
Lloyds Banking Group
Alice Genevois - Responsible AI Lead for Consumer Relationships, Lloyds Banking Group
Scaling Responsible AI is moving from theory to execution, as organisations look to embed governance directly into how AI is designed and deployed at scale. Alice Genevois and Suzanne Brink explore how organisations can scale AI responsibly through a central and business-led operating model. The session looks at what strong AI use cases look like from a Responsible AI perspective, and how to move beyond one-off governance reviews into reusable, embedded patterns that support day-to-day delivery. It also examines how central expertise and business ownership combine to enable innovation that is trusted, compliant, and scalable.
• Responsible AI scales through clear business ownership, enabled by strong central standards
• Reusable patterns and embedded controls accelerate delivery without increasing risk
• Effective partnership between central and business teams is critical to trust and accountability
10:30 am - 11:00 am
Morning Coffee Break and Speed Networking Session
Take a break, recharge, and make some new connections! This fast‑paced networking speed round gives you the chance to meet multiple peers over refreshments, exchange insights, and spark conversations you can continue throughout the event.
Morning Streamed Sessions
Stream A – Governance: Legal, Compliance, and Accountability
11:00 am - 11:30 am A Framework for AI Monitoring: Internal Metrics and External Risks Gerald Kierce - Co-Founder & CEO, TrustibleDeploying an AI system is not the finish line but the start of an ongoing obligation, one most organisations are not structured to meet. Effective oversight requires monitoring across two equally necessary surfaces: internal monitoring, which tracks cost, quality, drift, safety, and performance over time, and external monitoring, which captures vendor changes, public incidents, and evolving regulation. This session explores why AI monitoring is a genuinely hard problem and why most organizations only build for one side of it. It also examines why governing at the use-case level, rather than the model level, creates oversight that can withstand vendor swaps and mixed deployments.
- Implementing internal and external monitoring across two equally necessary surfaces.
- Governing use cases to maintain oversight through vendor and model changes.
- Evaluating cost, quality, drift, safety, and external risk signals.
Sponsored by: Trustible


Stream A – Governance: Legal, Compliance, and Accountability
11:30 am - 12:00 pm Panel Discussion – When Law Pushes and Governance Pulls: Closing the AI Accountability Gap Barbara Zapisetskaya - Principal Counsel, EBRDKirsten Van der Zwan - Chief Privacy Officer and Global Head of Privacy, AI & Digital Compliance, Signify
Gwen Morvan - Senior Legal Counsel, Synthesia
Nick Wild - Senior AI Governance Lead, Swift
AI regulation is accelerating, yet many organisations still struggle to translate legal obligations into effective, day to day governance. Under the EU AI Act and emerging standards frameworks, organisational functions including Legal and Governance are collectively responsible for risk classification, oversight, documentation, and organisational controls, but often approach these duties from different angles. This session explores how Legal and Governance teams can work together in practice: aligning responsibilities, streamlining AI use case triage, and building a shared governance model that stands up to regulatory scrutiny.
• Aligning legal and governance roles through shared ac-countability models
• Improving AI use case filtering to focus oversight where it matters most
• Strengthening collaboration by clarifying what Governance needs from Legal to operationalise compliance
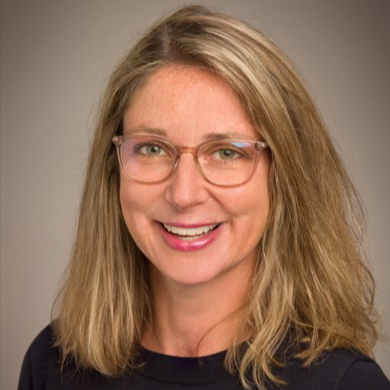
Kirsten Van der Zwan
Chief Privacy Officer and Global Head of Privacy, AI & Digital ComplianceSignify
Stream A – Governance: Legal, Compliance, and Accountability
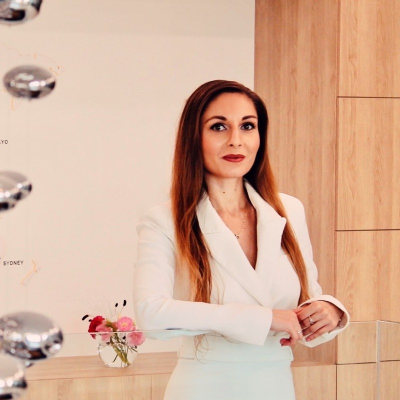
12:00 pm - 12:30 pm Presentation – Practical Ways to Manage Third Party and Privacy Risk at Scale Lucia Batlova - Senior Legal Counsel & EMEA Privacy Lead, LenovoAI driven innovation is accelerating, and with it, a surge of new tools, datasets, and experimental vendors vying for a place in the enterprise. Every promising partnership also carries potential privacy, security, and regulatory exposure. In this session, Lucia Batlova, Europe and META Data Protection & Privacy Lead at Lenovo, reveals how teams in a global organization cut through the noise: rapidly assessing high volume third party requests, screening risky AI initiatives without slowing momentum, and enabling safe experimentation at scale. With real world examples, she shows how legal can stay firmly positioned as an innovation accelerator, while keeping risk firmly in check (considering the fragmented global AI landscape & insufficiency of traditional privacy and security frameworks).
• Privacy and legal teams as innovation enablers: managing AI risk without unnecessarily slowing progress
• Reasonable expectations of privacy, transparency, and trust in AI deployments
• Third-party AI providers, vendor due diligence, and data-sharing considerations
• Data use limitations, purpose assessment, and appropriate safeguards
• Embedding privacy by design into AI and product development processes
Stream A – Governance: Legal, Compliance, and Accountability
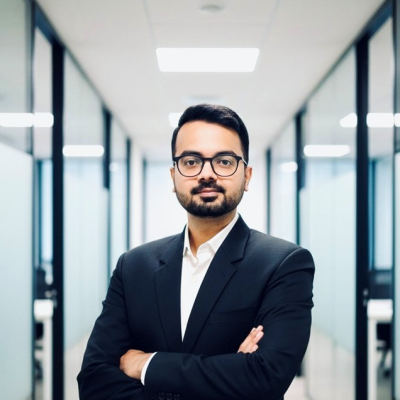
12:30 pm - 1:00 pm Panel Discussion – Embedding EU AI Act Governance: From Regulation to Real-World Implementation Pranav Gupte - Associate Director, AI Governance & Enablement, AstraZenecaLara Nogueira - Head of Responsible AI & Data Compliance, Ericsson
Gary Brown - Chief Privacy Officer, Westinghouse Electric Company
Oriana Medlicott - Responsible AI- EU Lead, Admiral Group
As the EU AI Act moves into its implementation phase, the focus is shifting from legislative ambition to operational delivery. Organisations must interpret risk classifications, conformity assessments and oversight duties, while aligning internal governance structures. This session offers a clear and practical update on timelines, enforcement trends and what regulators expect.
• Clarifying risk tiers and governance responsibilities.
• Aligning internal controls with supervisory scrutiny.
• Preparing for documentation, audit and enforcement readiness.
Stream B – Technical: Designing Governed Agentic Systems
11:00 am - 11:30 am Panel Discussion - Beyond the Framework: Embedding Trust into AIThe challenge is no longer defining principles but embedding them into delivery. Organisations have moved beyond governance frameworks and are now embedding operational capabilities such as AI risk management, monitoring, model assurance and run time controls directly into technology delivery. This panel discussion will explore the controls that actually work, how to remain in control of agents, and what organisations need to do now to prepare for the next wave of AI adoption.
Sponsored by: Capgemini
Stream B – Technical: Designing Governed Agentic Systems
11:30 am - 12:00 pm Presentation / Case Study – Designing Guardian Agents: A Taxonomy for Governing Multi-Agent AI Systems Alessandro Castelnovo - Head of Responsible AI, Intesa SanpaoloIn this technical case study, Alessandro Castelnovo, Head of Responsible AI at Intesa Sanpaolo, details how the bank designed and operationalised Guardian Agents to govern emerging multi-agent AI ecosystems. He presents a formal taxonomy that combines three operational roles (Reviewers, Monitors, and Protectors) with five structured risk domains: Data Security & Protection; Performance & Reliability; Quality & Compliance; Explainability & Transparency; and Ethical Coordination & Decisioning. The framework clarifies responsibilities, embeds automated safeguards, enables continuous oversight, and supports accountable, resilient orchestration across complex agent networks.
• Formalising operational roles define structured AI oversight mechanisms.
• Creating five risk domains that align governance with concrete control layers.
• Embedding safeguards to enable resilient, accountable multi-agent orchestration.
Stream B – Technical: Designing Governed Agentic Systems
12:00 pm - 12:30 pm Presentation – AI Governance Meets Security: Building an Organisational Model Robin Schoss - Director, AI Governance and Head of Information Security EMEA, Olympus- Olympus organisational model for AI governance and cybersecurity.
- Key collaboration challenges between governance and security teams.
- Embedding security controls into enterprise AI governance processes.
Stream B – Technical: Designing Governed Agentic Systems
12:30 pm - 1:00 pm Panel Discussion – Who Is the CEO of an Agent? Delegation, Agency & Responsibility Detlef Nauck - Head of AI & Data Science Research, BTOlu Akinyede - Data Privacy, Data Governance and AI Ethics, Aviva
Ramin Mobasseri - Head of Agentic AI Delivery, Wells Fargo
Rozemarijn Jens - Senior AI Innovation Lead, Shell
As enterprises delegate decisions to autonomous systems, they must confront a deeper question: what does it mean to transfer authority without severing responsibility? Agentic AI challenges traditional notions of control, oversight, and accountability, forcing organisations to redefine human agency in operational terms. This panel explores the philosophical and practical dimensions of delegation, and the skills required to remain meaningfully responsible for systems that act on our behalf.
• Examining delegation without severing human responsibility.
• Redefining agency in autonomous enterprise systems.
• Building skills for accountable human oversight.


Lunch
1:00 pm - 2:00 pm
Lunch in the Exhibition Hall: Network with your Peers
Afternoon Streamed Sessions
Stream A – Governance: Governing Autonomy at Scale
2:00 pm - 2:30 pm Session reserved for CredoAISponsored by: Credo AI

Stream A – Governance: Governing Autonomy at Scale
2:30 pm - 3:00 pm Presentation / Case Study – From Regulation to Automation: Scaling AI Governance Without Compliance Drift in the Research and Development Area of Novo Nordisk Per Rådberg Nagbøl - Senior Data & AI Governance Professional, Novo NordiskIn highly regulated sectors, such as life sciences, regulatory changes create a hidden risk: compliance drift, beyond the usual data drift. Hence, there is a need for practical strategies to keep AI aligned with evolving regulations and operational realities. This session will present the AI governance setup in the Research and Development area of Novo Nordisk. It will cover ideas, challenges, and practical solutions for automating AI governance without correspondingly scaling human labour.
• moving from regulation to automatable requirements and processes that enable the use of rule-, chatbot-, and agent-based automation.
• preventing compliance drift.
• making automation complement human labour.
• creating oversight of AI systems and visualise AI system interdependencies.
Stream A – Governance: Governing Autonomy at Scale
3:00 pm - 3:30 pm Data Governance vs AI Governance: Where Accountability Actually Sits Penny Jones - Responsible AI Lead, Zurich InsuranceTom Heath - Chief Data and AI Officer, Ward Williams
Matthew Sutton - AI Assurance Architect, Advai


Stream B – Technical: Explainability, Control & Engineering Reality
2:00 pm - 2:30 pm Session details to be announcedStream B – Technical: Explainability, Control & Engineering Reality
2:30 pm - 3:00 pm Presentation / Case Study – From Black Box to Glass Box: Making AI Outputs Defensible Pascal Hetzscholdt - Senior Director of AI Strategy and Content Integrity, WileyExplainability is often treated as a compliance afterthought; at Wiley, it is a system design requirement. At the scale of one of the world's largest scholarly publishers, that means AI outputs must be traceable, transparent about what models are trained on, clear on where human intervention sits in the workflow, and explicit about how updates and corrections are managed over time. In this session, Pascal Hetzscholdt, Director of AI Strategy and Content Integrity, provides a candid, technical look at how enabling students and researchers to prompt directly against curated, licensed content materially reduces hallucinations.
• Addressing cost pressures that drive unseen model changes.
• Securing meaningful quick wins while protecting long- term information integrity.
• Strengthening institutional situational awareness.
Stream B – Technical: Explainability, Control & Engineering Reality
3:00 pm - 3:30 pm Panel Discussion – Engineering vs Governance: Have We Got It Figured Out? Disha Mukherjee - Lead Data Engineer, Ford CreditGraham Ross - Head of Responsible AI, Centrica
Stephanie Cairns - Senior Data Scientist, AI Risk, OVO Energy
As AI systems scale and grow in complexity, the lines between engineering responsibility and governance oversight can blur. This panel explores where frictions emerge, how technical and governance teams can collaborate effectively, and whether current role definitions are fit for purpose. Through real-world examples, the discussion will probe whether enforcing policy-as-code and defining accountability truly resolves tension.
• Assigning clear roles to reduce friction and evolving with system complexity.
• Embedding governance into practice through technical pipelines.
• Integrating monitoring and checks to enforce accountability in real time.


Afternoon Plenary Session
3:30 pm - 4:00 pm
Afternoon Refreshment Break
4:00 pm - 4:30 pm
Breakout Session – Responsible AI Hot Takes
Tessa Darbyshire -
Head of AI Governance,
Informa
Caroline Ellis - AI & Data Ethics lead, NatWest Group
- Surfacing competing priorities that shape responsible AI decisions.
- Challenging assumptions through structured, balanced debate.
- Bridging technical, ethical, and strategic perspectives for better AI governance.
4:30 pm - 5:00 pm
Presentation - Responsible AI, Agentic Systems, and What Actually Scales
Daniel Hulme -
Chief AI Officer,
WPP
- A practical framework for AI and agentic adoption that cuts through the hype.
- Why governance and literacy are prerequisites for scaling - and how to frame that in terms the C-suite values.
- Augmenting, not replacing using AI and agents to unlock creative and commercial potential.
- The broader implications of these technologies for business and society.
5:00 pm - 5:30 pm
Afternoon Closing Panel Discussion – Faster Than We Think, Slower Than We Feel: The Real Pace of AI Adoption
Hellen Beveridge -
Head of AI Governance & Ethics,
AXA UK
Ramy Erfan - VP Business & Technology Enablement, Citi
Oliver Patel - Author of Fundamentals of AI Governance and OECD AI Expert Group, OECD
Mo Sadek - AI Security Practitioner, ALICE
Frontier AI capabilities continue to leap forward, reshaping expectations and recalibrating what "state of the art" means almost monthly. Yet inside most organisations, adoption remains steady, deliberate, and constrained by governance, infrastructure, and readiness. This widening gap creates strategic confusion: are we preparing for a world that's already here, or bracing for breakthroughs that won't materialise evenly? This session aims to disentangle technical progress from real‑world absorption capacity, clarify where agentic systems may genuinely transform workflows, and offer a pragmatic lens for prioritising business value amid hype cycles.
· Accelerating capability growth outpacing enterprise and policy absorption curves.
· Harnessing agentic systems where frontier advances drive real operational uplift.
· Prioritising durable shifts while filtering out performative or premature noise.